Alert Manager Enterprise
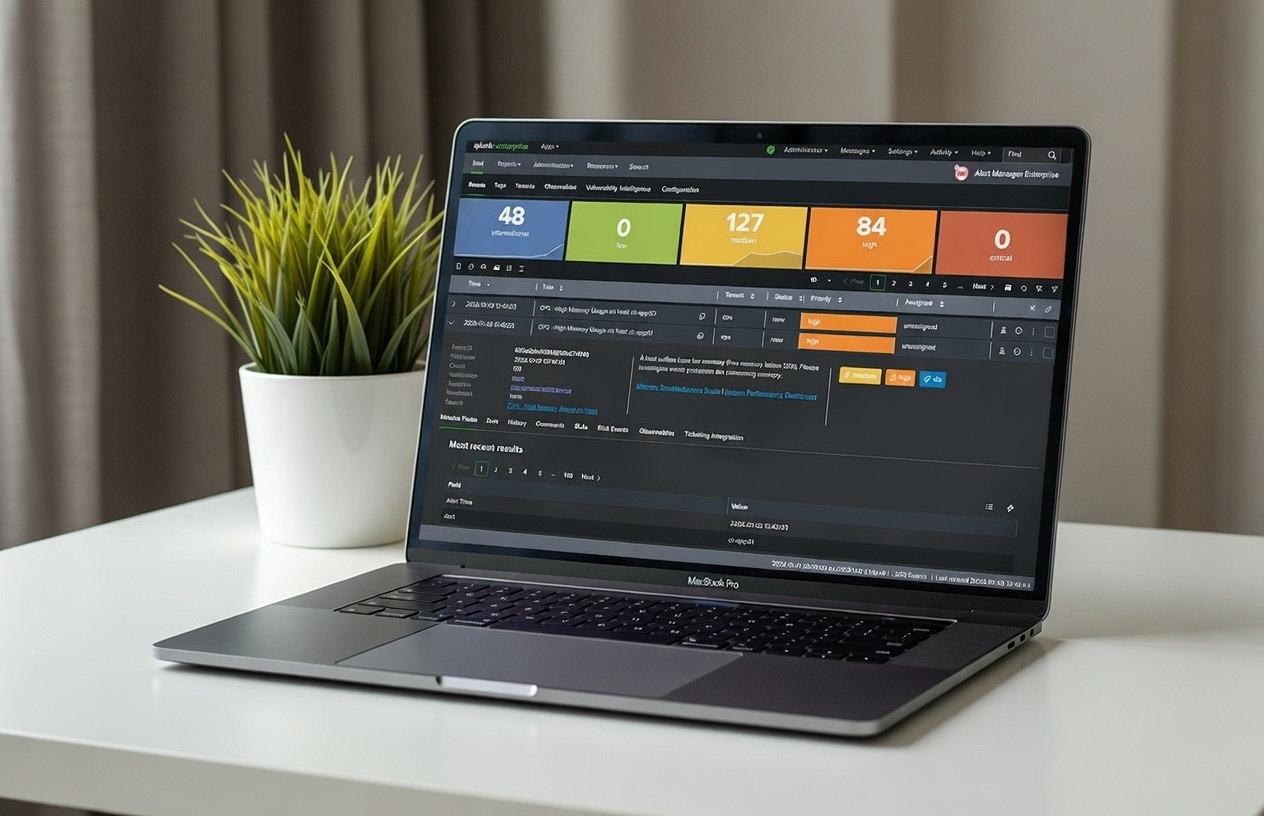
Splunk AppAlert Manager Enterprise turns Splunk alerts into events your team owns. Triage, assign and close them in Splunk.
Alert Manager Enterprise
Splunk AppAlert Manager Enterprise turns Splunk alerts into events your team owns. Triage, assign and close them in Splunk.
- Events, not noise: Every alert becomes an event with status, assignee, tags and history. Work them on the Events page.
- Context on every event: Assets and identities enrich each event. Risk Scoring adds up repeated alerts on the same host or user.
- Realizations in view: Vulnerability Intelligence shows which CVEs are present on which assets. Rules turn them into events.
ElasticSPL
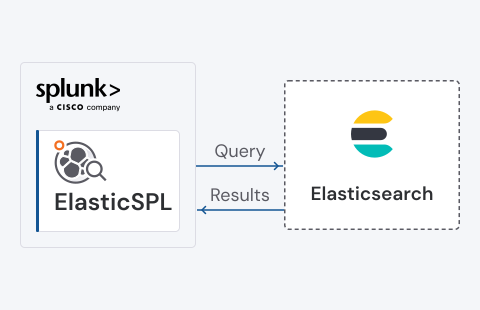
Add-on for SplunkElasticSPL Add-on for Splunk brings Elasticsearch into Splunk. Run Elasticsearch queries and see the results next to your Splunk data.
ElasticSPL
Add-on for SplunkElasticSPL Add-on for Splunk brings Elasticsearch into Splunk. Run Elasticsearch queries and see the results next to your Splunk data.
- One search bar: Run Elasticsearch queries from Splunk. No second console.
- Build and test fast: The ElasticSPL Workbench lets you build, test and preview DSL or Lucene queries.
- Ready for many clusters: Connect multiple Elasticsearch instances. Control who can query what.
S3SPL
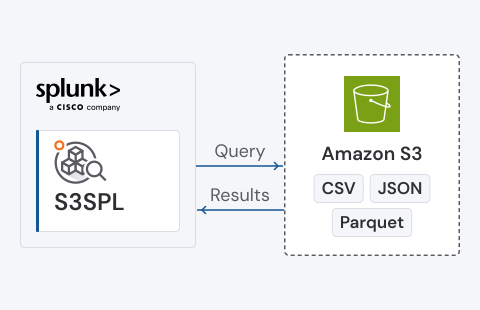
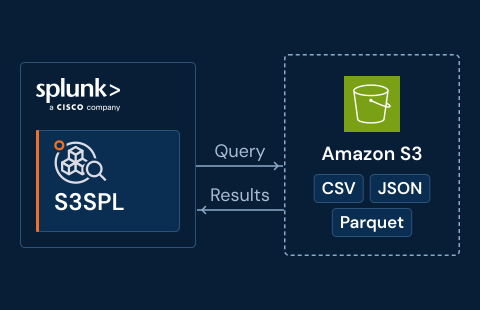
Add-on for SplunkS3SPL Add-on for Splunk queries your Amazon S3 data from Splunk. No ETL, no downloads, no extra infrastructure.
S3SPL
Add-on for SplunkS3SPL Add-on for Splunk queries your Amazon S3 data from Splunk. No ETL, no downloads, no extra infrastructure.
- Query in place: Search CSV, JSON and Parquet files in S3 straight from Splunk.
- Native to Splunk: Use custom commands and dashboards to explore S3 data where you already work.
- Costs up front: See the estimated query cost before you run it. Manage many buckets with role-based access.
Cribl
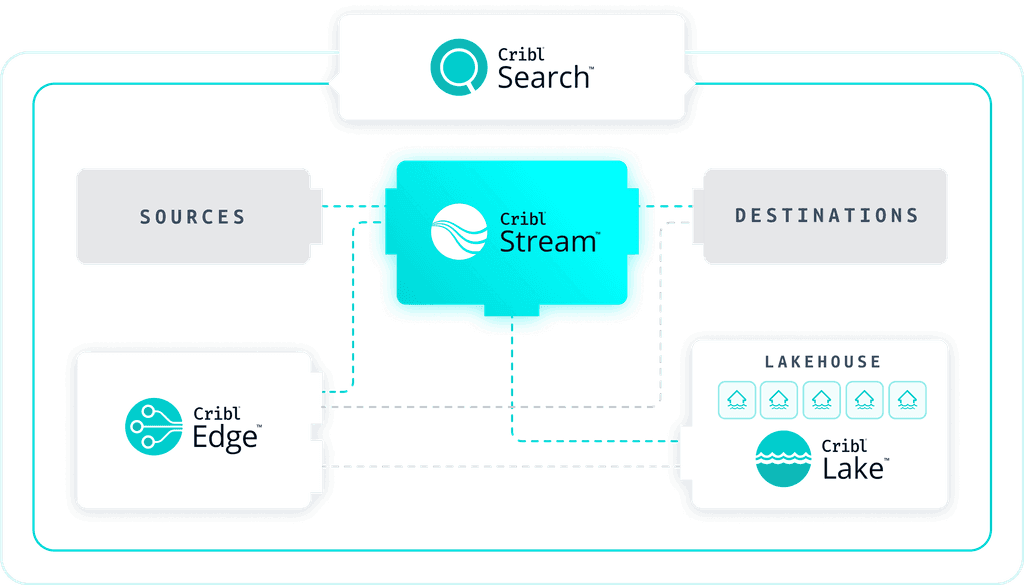
Technology PartnerWe run Splunk and Cribl side by side for our customers. We plan, build and tune your Cribl Stream pipelines.
Cribl
Technology PartnerWe run Splunk and Cribl side by side for our customers. We plan, build and tune your Cribl Stream pipelines.
- Splunk and Cribl expertise: One team that knows both platforms. We design how data moves between Splunk and Cribl Stream.
- Pipelines that fit your Splunk: We route, shape and reduce data in Cribl Stream before it reaches your indexes.
- Design and rollout help: We help you plan your Cribl Stream setup and bring your Splunk data sources over step by step.
Outcold Solutions
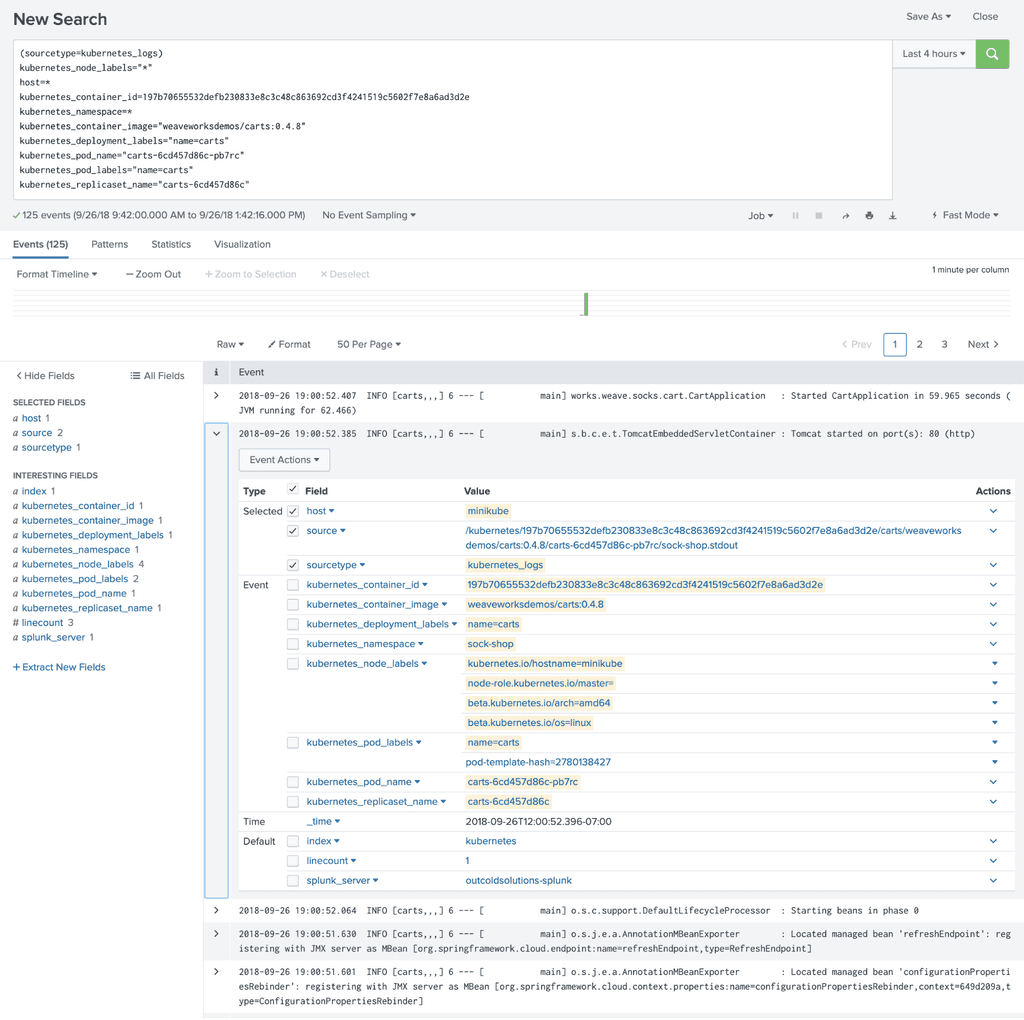
Technology PartnerFull Kubernetes and container observability. Monitor containerized environments with logs, metrics, and events via Splunk.
Outcold Solutions
Technology PartnerFull Kubernetes and container observability. Monitor containerized environments with logs, metrics, and events via Splunk.
- Kubernetes-native Observability: Monitor containerized environments with full access to logs, metrics, and events via Splunk.
- Instant Insights: Leverage powerful dashboards and search capabilities to troubleshoot and analyze cluster performance in real time.
- Seamless Splunk Integration: Stream data directly into Splunk from Kubernetes and OpenShift without additional agents or complexity.
Ready to Tackle Your Data Challenges?
From security threats to complex analytics, we're here to turn your data challenges into opportunities.